7 Key Cybersecurity Services Mount Laurel Businesses Need in 2026
Mount Laurel businesses face a rising volume of digital threats that target local commercial corridors and industrial operations. Rivell provides cybersecurity services to New Jersey organizations, helping them reduce risk, protect sensitive data, and strengthen operational resilience. This list outlines the essential security components that form a defensible digital perimeter for companies in Burlington County.
1. Proactive Threat Detection and Response
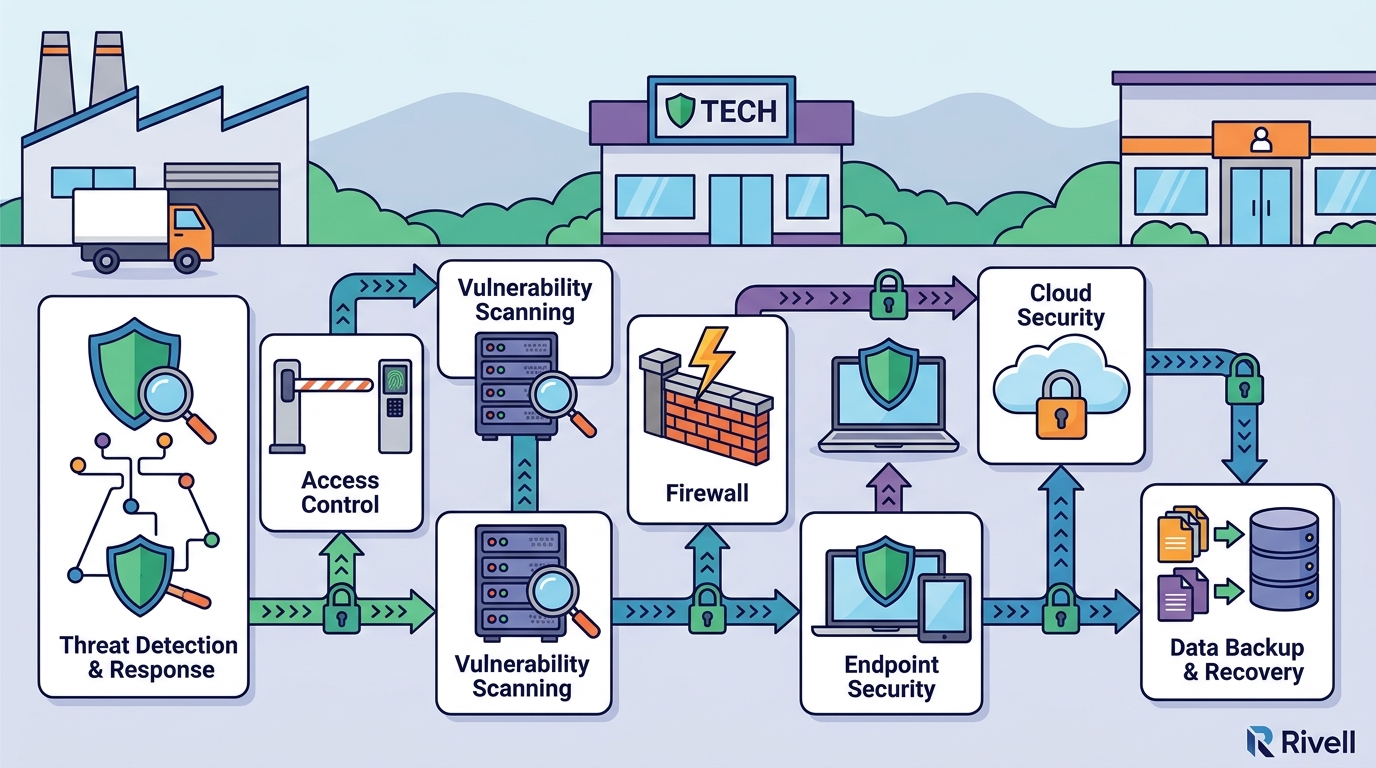
Continuous monitoring identifies anomalies before they escalate into full-scale breaches. Where 24/7 monitoring is included in the service scope, configured signals from networks, systems, endpoints, and cloud services can be reviewed under documented triage and escalation procedures. Coverage depends on the connected tools, available telemetry, access, contacts, and response responsibilities. It does not guarantee that every threat will be detected or contained immediately, but it significantly reduces the window of exposure.
2. Endpoint Protection and Management
Securing individual devices is the first line of defense against malware and ransomware. Endpoint protection involves deploying antivirus software, firewalls, and intrusion detection systems on every workstation, server, and mobile device. This multi-layered approach ensures that if one device is compromised, the threat is isolated and cannot spread across the broader network. Regular patch management is also critical to closing known vulnerabilities in operating systems and applications.
3. Network Security and Infrastructure Hardening
A secure network architecture prevents unauthorized access to internal systems. Network security focuses on protecting the data in transit and the infrastructure that supports it. This includes configuring firewalls, segmenting networks to limit lateral movement, and implementing secure remote access protocols. For businesses in Mount Laurel that rely on stable connectivity for logistics and distribution, a hardened network ensures that operational data remains protected from external intrusions.
4. Cloud Security and Access Controls
Protecting cloud environments requires strict identity and access management. As businesses migrate to cloud platforms, the perimeter of security shifts from physical boundaries to digital identities. Cloud security involves configuring permissions, enforcing multi-factor authentication, and monitoring cloud service usage. It is essential to ensure that only authorized personnel can access sensitive data stored in cloud tenants, preventing data leaks and unauthorized modifications.
5. Data Backup and Disaster Recovery
Recoverability after an incident depends on the integrity and availability of backups. The CISA #StopRansomware Guide recommends offline, encrypted backups and regular testing of backup availability and integrity. Buyers should ask whether backup, restore testing, incident response, and recovery coordination are included in the same scope or assigned to separate providers. A robust disaster recovery plan ensures that business operations can resume quickly after a ransomware attack or system failure.
6. Security Awareness and Human Firewall Training
Employees are often the most targeted vector in social engineering attacks. Security awareness training educates staff on how to identify phishing emails, suspicious links, and social engineering tactics. Building a human firewall involves creating a culture of vigilance where employees report potential threats immediately. This soft control is a critical component of any cybersecurity strategy, as technical controls alone cannot stop a determined attacker who manipulates human behavior.
7. Compliance Support and Risk Assessment
Regular risk assessments ensure that security measures align with industry regulations. Cybersecurity is inherently linked to risk management, involving the identification of potential threats and the assessment of their impact. Compliance support helps organizations meet legal, regulatory, and contractual obligations, such as HIPAA for healthcare providers or SOC 2 for technology firms. A documented risk assessment provides a clear roadmap for prioritizing security investments and mitigating high-value asset risks.
Choosing the Right Cybersecurity Services
Selecting the right combination of services depends on your specific business processes, data sensitivity, and regulatory environment. Start by documenting your current environment, including users, sites, critical applications, and known end-of-support technology. Then, identify which business processes cannot tolerate an extended interruption. A managed IT provider can help you align these operational needs with the appropriate security controls.
Frequently Asked Questions
What is the most important cybersecurity service for a small business?
Endpoint protection and data backup are often the most critical services for small businesses. These two components address the most common attack vectors and provide a safety net in the event of a ransomware incident. Without reliable backups, a small business may not be able to recover from a severe data loss event.
How often should a business conduct a cybersecurity risk assessment?
Businesses should conduct a formal risk assessment at least annually or whenever there are significant changes to the IT infrastructure. Regular assessments help identify new vulnerabilities and ensure that existing controls remain effective against evolving threats. This proactive approach is recommended by NIST for small businesses to maintain a strong security posture.
Does Rivell provide cybersecurity services in Mount Laurel?
Yes, Rivell provides cybersecurity services to businesses in Mount Laurel, NJ, and the surrounding Burlington County business corridor. The company offers proactive threat detection, endpoint protection, and cloud security tailored to the needs of local organizations. Rivell has supported small and medium-sized businesses across New Jersey since 1997.
What is the difference between cybersecurity and network security?
Cybersecurity is a comprehensive term that encompasses the protection of all computer systems, networks, and data from theft or damage. Network security is a specific subset of cybersecurity that focuses on protecting the data in transit and the infrastructure that supports it. While related, cybersecurity covers a broader range of threats, including those targeting individual devices and applications.
How can a business reduce its risk of a ransomware attack?
Businesses can reduce ransomware risk by implementing offline, encrypted backups and regular testing of backup availability. The CISA #StopRansomware Guide emphasizes the importance of these practices to ensure that data can be restored without paying a ransom. Additionally, keeping software up to date and training employees on phishing prevention are key defensive measures.
What role does a Virtual CISO play in a business's security strategy?
A Virtual CISO provides expert cybersecurity leadership and strategic guidance without the cost of a full-time executive. They help define security policies, oversee risk management, and ensure that the organization's security posture aligns with its business objectives. This service is particularly useful for small and mid-sized businesses that need high-level security oversight but lack the resources to hire a dedicated CISO.
Partner with Rivell for Comprehensive Cybersecurity
Protecting your business in Mount Laurel requires a strategic approach to cybersecurity that addresses both technical and human factors. Rivell offers customized cybersecurity services to help New Jersey organizations reduce risk, protect sensitive data, and strengthen operational resilience. To discuss your current security posture and explore how Rivell can support your business, today.